
Metasploit Framework 6.4.92 (macOS, Linux, Windows) - 开源渗透测试框架
 Metasploit Framework 6.4.92 (macOS, Linux, Windows) - 开源渗透测试框架
Rapid7 Penetration testing, updated Oct 10, 2025
请访问原文链接:https://sysin.org/blog/metasploit-framework-6/ 查看最新版。原创作品,转载请保留出处。
作者主页:sysin.org
世界上最广泛使用的渗透测试框架
知识就是力量,尤其是当它被分享时。作为开源社区和 Rapid7 之间的合作,Metasploit 帮助安全团队做的不仅仅是验证漏洞、管理安全评估和提高安全意识 (sysin);它使防守队员能够始终领先比赛一步(或两步)。
新增功能
主要版本的新特性请参看:Metasploit Framework 6.4 Released, Mar 25, 2024
🛰️ Metasploit 周报 · 2025 年 10 月 9 日
📅 发布日期:2025 年 10 月 10 日
✅ Meterpreter:为 Windows ARM64 启动并减少内存占用
此次 Metasploit-Framework 发布包含了对我们载荷能力的两个重要里程碑。第一个由社区贡献者 Alexander “xaitax” Hagenah 牵头,是对我们的 ReflectiveLoader 的增强——这是我们 Windows 植入器中用于支持 ARM64 二进制文件的关键组件。此关键更新不仅是一次增量改进,而是朝着开发并实现原生 ARM64 Windows Meterpreter 的未来迈出的基础性一步。
通过我们的 ReflectiveLoader 加载并执行 Windows ARM64 二进制文件的能力为工具开发开辟了新途径,并延续了项目将工具集扩展到更多现代计算架构的承诺。随着基于 ARM 的处理器在 Windows 环境中的采用持续增长,我们预计该增强将对开发者和用户极具价值。第二个里程碑是将标准扩展(stdapi)拆分为可以单独加载的子组件扩展。完整的 stdapi 扩展以前(并且现在仍然)默认自动加载,以扩展 Meterpreter 在系统内的功能 (抄si袭quan者jia)。
当前的变更允许高级用户选择不加载完整的 stdapi 扩展,而改为加载一个或多个更小、更轻量的子扩展,这些子扩展包含与 stdapi 方法主题相近的子集:
stdapi_audio:管理与音频相关的任务,例如在远程系统上播放声音。
stdapi_fs(文件系统):处理文件系统操作,包括目录导航、文件编辑以及文件传输。
stdapi_net(网络):便利网络操作,提供检索网络配置与设置隧道通道(例如端口转发)等命令。
stdapi_sys(系统):对本地与远程进程执行操作,为后渗透模块提供低级 API 用以分配与写入内存区域、执行远程线程以及调查进程。stdapi_railgun:使基于我们协议 Railgun 开发的后渗透模块能够执行 (sysin)。此子组件授予对 Windows API 函数的低级访问,允许灵活地链式调用这些函数。stdapi_ui(用户界面):扩展 Meterpreter 的功能以收集桌面环境信息,例如枚举窗口与截屏。stdapi_webcam(Webcam/摄像头):提供对系统中已安装摄像头的访问,支持拍摄摄像头快照等操作。
要使用新的标准 API,可以按以下流程操作:启动 msfconsole 并选择其中一个 windows meterpreters,例如 use payload/windows/x64/meterpreter/reverse_tcp
通过执行 set AutoLoadExtensions ‘’ 来移除自动加载的扩展。
现在在目标系统上生成并执行 payload。在 meterpreter 会话内,使用 load stdapi_<subcomponent> 加载任意子组件,例如:
msf payload(cmd/windows/http/x64/meterpreter/reverse_tcp) > sessions -i -1
[*] Starting interaction with 1...

meterpreter > sysinfo
[-] The "sysinfo" command requires the stdapi extension to be loaded or the relative subcomponent (run: `load stdapi` or `load stdapi_audio/_fs/_net/_sys/_railgun/_ui/_webcam`)
meterpreter > load stdapi_sys
Loading extension stdapi_sys...Success.
meterpreter > sysinfo
Computer        : WIN10_22H2_7FD2
OS              : Windows 10 22H2+ (10.0 Build 19045).
Architecture    : x64
System Language : en_US
Domain          : WORKGROUP
Logged On Users : 2
Meterpreter     : x64/windows
meterpreter >
🆕 新模块内容(2 个)
Listmonk 不安全的 Sprig 模板函数导致环境变量泄露
- 作者:Tarek Nakkouch
- 类型:辅助(Auxiliary)
- Pull request: #20579(贡献者:nakkouchtarek)
- 路径:
gather/listmonk_env_disclosure - AttackerKB 参考:CVE-2025-49136
- 描述:此模块新增了一个辅助扫描模块,用于检测 Listmonk ≥ v4.0.0 且 < v5.0.2 中的不安全模板函数漏洞。该漏洞允许具有最小权限的已认证用户通过活动模板预览读取主机上的任意环境变量 (sysin)。Listmonk 部署中的环境变量通常包含诸如数据库凭证、SMTP 密码、API 密钥和管理员凭证等敏感信息,可能导致系统被完全攻破。
恶意 Windows Script Host 脚本文件(.wsf)
- 作者:bcoles bcoles@gmail.com
- 类型:利用模块(Exploit)
- Pull request: #20586(贡献者:bcoles)
- 路径:
windows/fileformat/windows_script_host_wsf - 描述:新增了一个 Windows 文件格式模块,能够生成恶意的 Windows Script Host 文件。
✨ 增强与新功能(3 项)
- #20527 来自 h00die — 将 plist 利用模块移动到新的 persistence 目录。它利用了持久化模块的新功能,通过添加 persistence mixin 实现。
- #20568 来自 bcoles — 添加了一个用于 VBS 载荷混淆的新库,并更新了
windows/fileformat/windows_script_host_vbscript模块以使用该新库。 - #20595 来自 zeroSteiner — 向 331 个不同模块添加了缺失的 CVE 条目 (sysin)。
- #19975 来自 dledda-r7 — 将
stdapi扩展拆分为可单独加载的子组件,以减小 Windows Meterpreter 载荷在内存中的占用。原始的stdapi扩展仍可加载,且在 Windows Meterpreter 载荷加载时自动加载stdapi的默认行为仍保持不变。
🐞 修复的 Bug(2 项)
- #20563 来自 jheysel-r7 —
ldap_esc_vulnerable_cert_finder在运行注册表检查时现在会检查 CA 与 DC。 - #20582 来自 xHector1337 — 修复了随机标识符库的回归,该回归在处理 PHP 代码时导致失败。
版本比较
Open Source: Metasploit Framework
下载:Metasploit Framework 6.4.92 (macOS, Linux, Windows) - 开源渗透测试框架
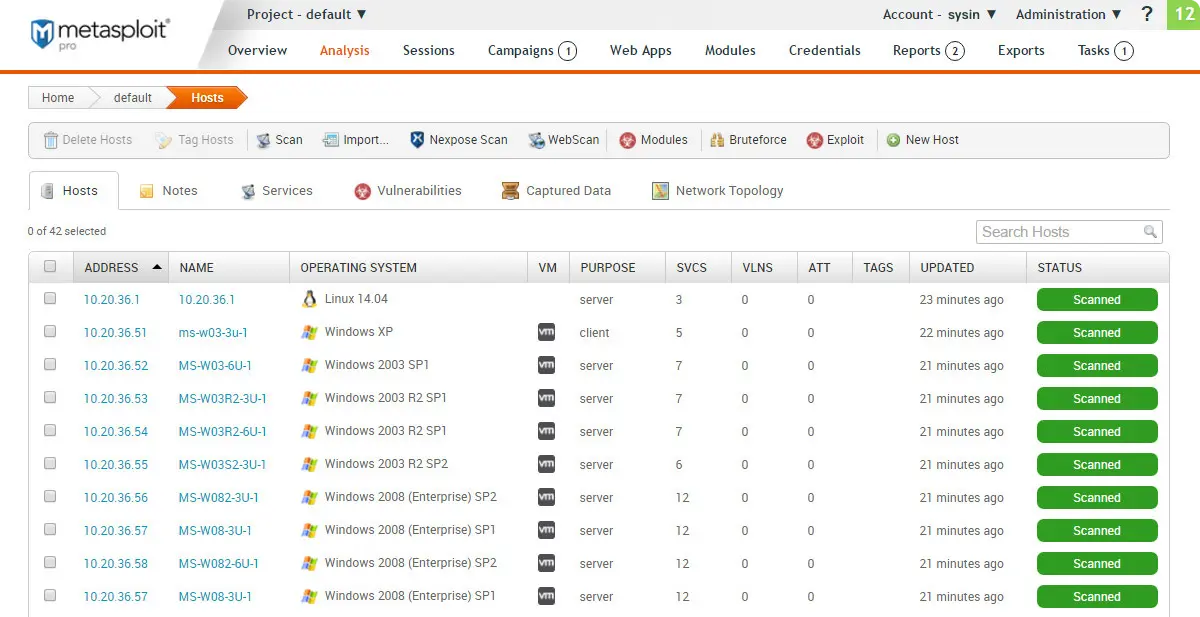
Commercial Support: Metasploit Pro
| All Features | Pro | Framework |
|---|---|---|
| - Collect | ||
| De-facto standard for penetration testing with more than 1,500 exploits | ✅ | ✅ |
| Import of network data scan | ✅ | ✅ |
| Network discovery | ✅ | ❌ |
| Basic exploitation | ✅ | ❌ |
| MetaModules for discrete tasks such as network segmentation testing | ✅ | ❌ |
| Integrations via Remote API | ✅ | ❌ |
| - Automate | ||
| Simple web interface | ✅ | ❌ |
| Smart Exploitation | ✅ | ❌ |
| Automated credentials brute forcing | ✅ | ❌ |
| Baseline penetration testing reports | ✅ | ❌ |
| Wizards for standard baseline audits | ✅ | ❌ |
| Task chains for automated custom workflows | ✅ | ❌ |
| Closed-Loop vulnerability validation to prioritize remediation | ✅ | ❌ |
| - Infiltrate | ||
| Basic command-line interface | ❌ | ✅ |
| Manual exploitation | ❌ | ✅ |
| Manual credentials brute forcing | ❌ | ✅ |
| Dynamic payloads to evade leading anti-virus solutions | ✅ | ❌ |
| Phishing awareness management and spear phishing | ✅ | ❌ |
| Choice of advance command-line (Pro Console) and web interface | ✅ | ❌ |
下载地址
Metasploit Framework 6.4.x (macOS, Linux, Windows)
macOS:metasploit-framework-VERSION.x86_64.dmg
Windows:metasploit-framework-VERSION-x64.exe
Debian/Ubuntu:
Linux deb x64:metasploit-framework_VERSION_amd64.deb
Linux deb x86:metasploit-framework_VERSION_i386.deb
Linux deb arm64:metasploit-framework_VERSION_arm64.deb
Linux deb armhf (hard float):metasploit-framework_VERSION_armhf.deb
RHEL/Fedora:
Linux rpm x64:metasploit-framework-VERSION.el6.x86_64.rpm
相关产品:Metasploit Pro 4.22.8-2025091701 (Linux, Windows) - 专业渗透测试框架
更多:HTTP 协议与安全

 浙公网安备 33010602011771号