
金和 c6 sql注入漏洞分析
这里分析的对应漏洞为:金和 C6 协同管理平台 IncentivePlanFulfill.aspx SQL注入
在网上下载好源码打开后发现其为发布包(DLL + 前端资源)
所以用软件dnspy进行反编译
这里金和 C6 协同管理平台 IncentivePlanFulfill.aspx SQL注入 相对应的漏洞点在于
GET /C6/JHSoft.Web.IncentivePlan/IncentivePlanFulfill.aspx/?IncentiveID=1WAITFOR+DELAY+%270:0:6%27--&TVersion=1 HTTP/1.1
所以直接加载相应的dll进行反编译
打开后根据poc里的路径对应到JHSoft.Web.IncentivePlan空间 下面的ncentivePlanFulfill类
在页面下需要找寻poc里面的两个参数IncentiveID 以及 TVersion是如何传入的
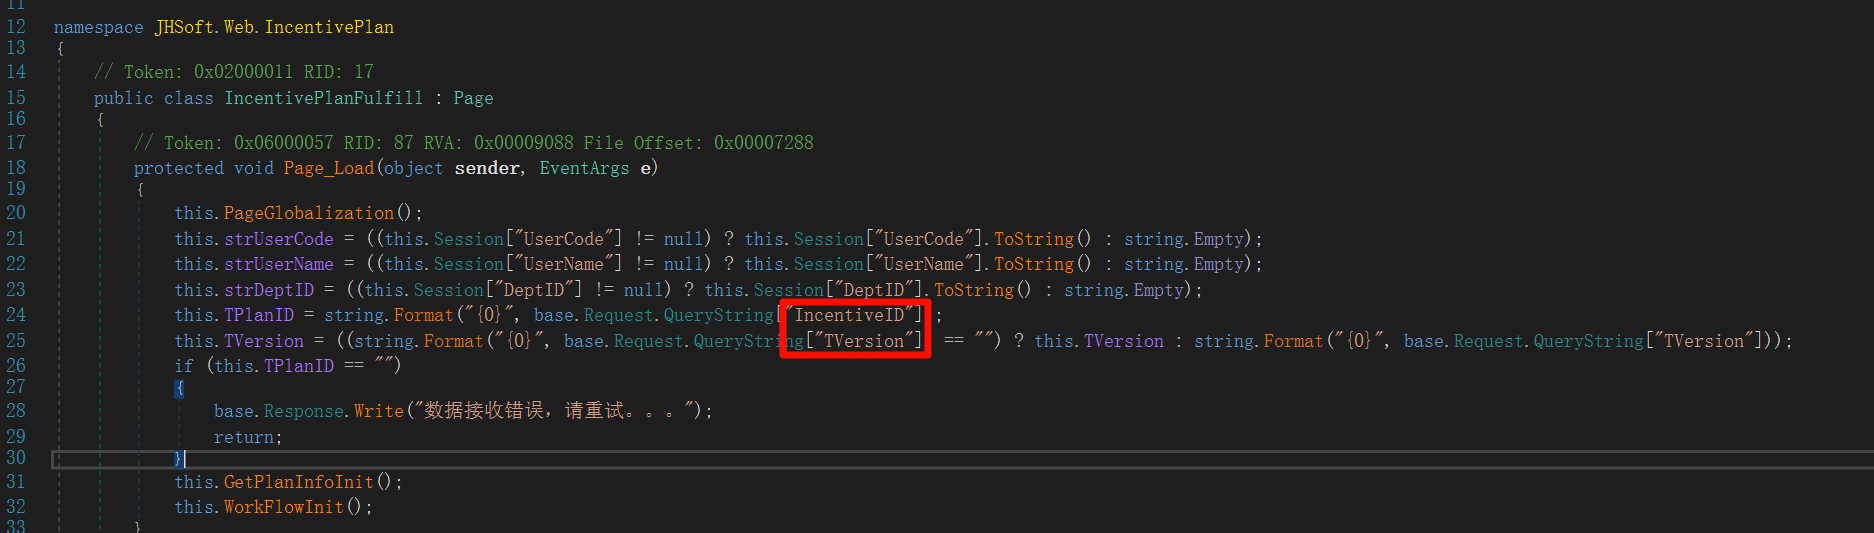
this.TPlanID  = string.Format("{0}", base.Request.QueryString["IncentiveID"]);
this.TVersion = ((string.Format("{0}", base.Request.QueryString["TVersion"]) == "")
                    ? this.TVersion
                    : string.Format("{0}", base.Request.QueryString["TVersion"]));
这里直接读取了两个变量的值最后进行this.GetPlanInfoInit();传递
追踪GetPlanInfoInit跳转到第二部分
还是找这两个变量(TVersion和IncentiveID)
private void GetPlanInfoInit()
{
    JHSoft.IncentivePlan.BLL.IncentivePlan incentivePlan = new JHSoft.IncentivePlan.BLL.IncentivePlan();
    JHSoft.IncentivePlan.Model.IncentivePlan incentivePlanMessageById = incentivePlan.GetIncentivePlanMessageById(this.TPlanID, this.TVersion);
}
分析代码,首先是创建了一个实例,来调用相关方法
然后根据页面传入的计划ID和版本号,获取这条激励计划的详细信息
所以追踪GetIncentivePlanMessageById 跳转到第三部分
JHSoft.IncentivePlan.DAL.IncentivePlan incentivePlan2 = new JHSoft.IncentivePlan.DAL.IncentivePlan();
string appFlagById = incentivePlan2.GetAppFlagById(this.TPlanID, this.TVersion);
到了第三部分发现这里实际上是对PlanID 是否为空字符进行判断
而核心GetIncentivePlanMessageById 在 BLL(业务逻辑层) 里
所以追踪GetIncentivePlanMessageById到第四部分
这里的核心代码就是
stringBuilder.Append("select IncentiveID,IncentiveVersion,IncentiveTitle,IncentiveContent,IncentiveYear,IncentivePeriod,IncentiveType,CreateUser,CreateTime,IncentiveTemplet,AppFlag,FulfillContent,FulfillMark,FulfillUser,FulfillTime,DelFlag,GrantDept,GrantUser,IncentiveDept,IncentiveUser,IncentiveTargetDesc,IsCurrentVersion");
stringBuilder.Append(" FROM IncentivePlan ");
if (TPlanID.Trim() != "")
{
    stringBuilder.Append(" where IncentiveID=" + TPlanID + " and IncentiveVersion=" + TVersion);
}
这里就是创建一个空的 IncentivePlan 对象然后用StringBuilder 拼接 SQL 语句
核心问题:
-
TPlanID和TVersion是用户可控输入(来自 URL QueryString)。 -
直接用
+拼接到 SQL 字符串里。 -
没有使用参数化查询。
总结
IncentivePlanFulfill 页面的 Page_Load 里base.Request.QueryString["IncentiveID"]和base.Request.QueryString["TVersion"]通过URL QueryString ,请求用户输入的TPlanID 和 TVersion
之后调用var plan = incentivePlan.GetIncentivePlanMessageById(this.TPlanID, this.TVersion);
把用户输入的 TPlanID 和 TVersion 直接传给业务逻辑层(BLL),然后 BLL 又传给 DAL 执行 SQL 查询
整合过程没有任何过滤或者类型检查从而导致用户输入直接影响 SQL 语句
tips:

 浙公网安备 33010602011771号